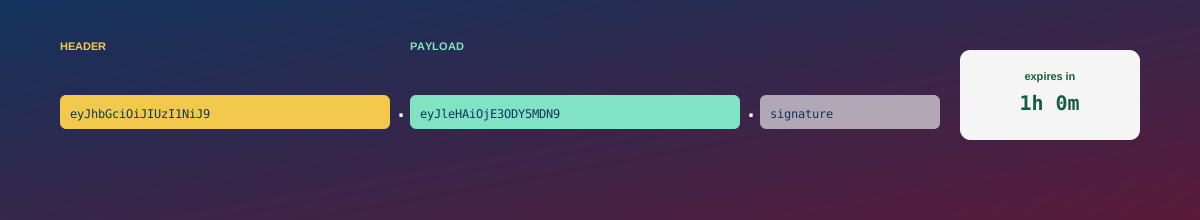
Paste a JWT below to decode its header/payload and check its expiry. Runs entirely in your browser — a token is a live credential, so nothing here is ever sent anywhere.
header.payload.signature, each part (except the signature) base64url-encoded JSON. Decoding just reverses that encoding — no cryptography involved.curl -sS "https://devops.majbase.com/jwt-checker/api" \
--data-urlencode 'token=eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9....'Returns {"header", "payload", "time_claims", "expiry_status": {"expired","diff_seconds"}|null, "not_before_status": {"active","diff_seconds"}|null, "has_signature"}, or {"error": "..."} for a malformed token. Decode only — the signature is never verified.
Want an AI agent (Claude Code, claude.ai, or anything else that supports the Agent Skills format) to use this tool for you on request? Download the skill below and add it:
~/.claude/skills/jwt-checker/SKILL.md