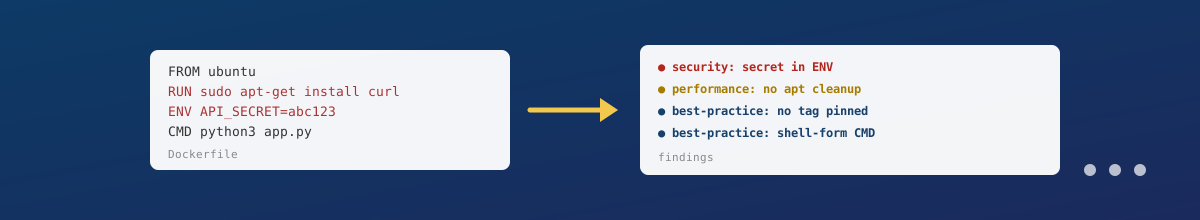
Paste a Dockerfile and get rule-based findings across three categories: security (secrets baked into ENV/ARG, root user, unverified curl-pipe-to-shell), performance (missing apt/pip cache cleanup, unpinned recommends), and best-practice (unpinned base image tags, ADD vs COPY, shell-form CMD, missing HEALTHCHECK). Fixed rules, not an LLM — deterministic and free, like every other tool on this site. Runs entirely in your browser.
curl -sS -X POST https://devops.majbase.com/dockerfile-analyzer/api -H "Content-Type: application/json" --data-binary @- <<'EOF'
{"dockerfile": "FROM ubuntu\nRUN apt-get install -y curl\nCMD python3 app.py"}
EOF
Returns {"findings": [{"line", "severity", "rule", "message"}, ...], "counts": {...}, "total": N}, or {"error": "..."}.
Want an AI agent (Claude Code, claude.ai, or anything else that supports the Agent Skills format) to use this tool for you on request? Download the skill below and add it:
~/.claude/skills/dockerfile-analyzer/SKILL.md