Badge or Biometric Access
Back to Data Center Management · Access Logging · Visitor and Vendor Tracking · Cage or Rack-Level Restriction · Service Offerings
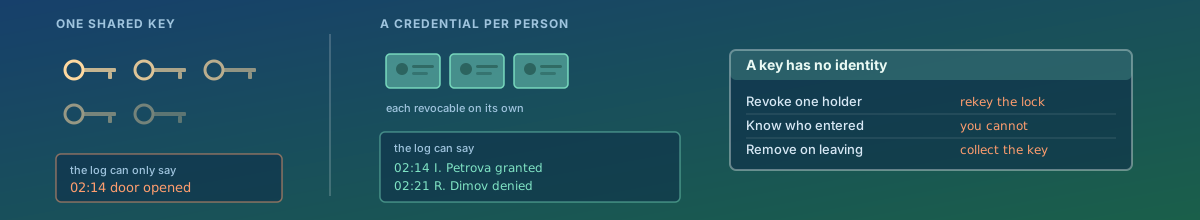
This is entry restricted to people who actually need it, not a shared key everyone has a copy of. The contrast in that sentence is the whole argument, and it is not really about convenience.
1. A Key Has No Identity
A mechanical key authenticates nothing. It proves only that whoever turned it was holding a piece of metal, and metal does not record who carried it. Three consequences follow, and all three are the reason this control exists.
- You cannot revoke one holder. Removing access from one person means rekeying the lock and reissuing to everyone else — so in practice nobody does it, and the key stays out.
- You cannot say who entered. The best any log can offer is that the door opened. When something has to be investigated, that is the end of the enquiry.
- You cannot be sure it came back. Keys are copied at any hardware shop, and a returned key is not evidence that no copy exists.
A per-person credential fixes all three at once, which is why this is worth doing even in a small room with five people in it.
2. Not All Badges Are Equal
The most common mistake is treating a badge system as solved because badges exist. The underlying card technology decides whether the credential means anything.
| Technology | What it does | Status |
|---|---|---|
| 125 kHz proximity | Broadcasts a fixed number to any reader that asks. No authentication at all | Cloned in seconds with a cheap handheld copier. Treat as a label, not a credential |
| Magnetic stripe | Static data, read and written with commodity hardware | Equivalent to the above |
| 13.56 MHz smartcard with mutual authentication | Card and reader prove themselves to each other with diversified keys; the exchange differs every time | The current baseline. DESFire EV2 or EV3, Seos and similar |
| Phone-based credential | Credential in a secure element, usually with the phone's own unlock as a second factor | Good, and issued and revoked without anyone handling plastic |
If you inherit a site, find out which of these you have before anything else. A building full of 125 kHz cards has the appearance of access control and the security of a shared key, with the added disadvantage that everyone believes it is solved.
3. Biometrics Solve One Problem and Create Another
Biometrics answer the question a card cannot: whether the credential is being used by the person it was issued to. That is genuinely valuable at the door of a room full of other people's data. They come with constraints that are easy to discover too late.
- A fingerprint cannot be reissued. If a template is compromised there is no equivalent of changing a password. This argues for storing templates rather than images, and for keeping them on the reader or on the card rather than in a central database.
- They are special-category personal data. Under the GDPR, biometric data processed to identify someone uniquely sits under Article 9: you need a lawful basis for it specifically, and a data protection impact assessment is the normal expectation. Plan for that before procurement, not after.
- Offer an alternative. Some people cannot reliably enrol, and some will object. A system with no fallback becomes a system people prop doors open around.
- They are better as a second factor. Card plus fingerprint at the door of a sensitive area is a strong, proportionate arrangement. Biometric alone, with no card, puts the whole weight of entry on a sensor with a false-accept rate.
4. The Part That Actually Fails Is Removal
Almost no breach of physical access control involves defeating a reader. It involves a credential that should have stopped working months ago and did not.
- Leavers. Access revocation has to be a step in offboarding, triggered by HR rather than by someone remembering. Same-day, and for involuntary departures, before the conversation.
- Movers. The quiet one. People change roles and accumulate access, because adding is a request and removing is nobody's job.
- Contractors. Issue with an expiry date set at issue. A credential that expires by default is the only kind that reliably goes away.
- Periodic review. Someone who owns the room reviews the list of people with access, on a schedule, and signs it. This is also precisely what an auditor will ask for — see ISO 27001 and SOC 2 and the SOC 2 Evidence Helper.
5. Scope the Access, Not Just the Person
- By zone. Access to the building is not access to the data hall, and access to the hall is not access to your cabinets. See cage or rack-level restriction.
- By time. Most staff have no reason to enter at 03:00. Time-of-day restrictions cost nothing and turn an out-of-hours entry into something that had to be arranged deliberately.
- Two people for the most sensitive areas, where the risk justifies it.
6. What the Reader Cannot Enforce
- Tailgating. One badge, two people through the door, and the system records one entry. Mantraps or turnstiles are the engineering answer; where those do not exist, the answer is a stated expectation that people do not hold the door, and a log that is actually read.
- Anti-passback helps: a credential that entered and never exited cannot enter again, which surfaces both tailgating and passed-around cards.
- Egress must never depend on the system. Fire regulations require free exit, and a door that could trap someone during a power failure is not a security control, it is a hazard. Decide fail-safe or fail-secure per door, deliberately, with the fire strategy.
- Doors held open. A door-ajar alarm is cheap and catches the propped fire door that defeats everything above it.
How We Approach It
- Establish what the credentials actually are — card technology first, because a 125 kHz estate changes the priorities entirely.
- Pull the current access list and reconcile it against HR. The leavers still holding access are usually the first concrete finding.
- Define zones and who needs each, including time-of-day limits.
- Wire revocation into joiners, movers and leavers, with expiry by default for contractors.
- Decide where a second factor is proportionate, and handle the data protection work if that factor is biometric.
- Set the review cadence, and connect the system to logging so that entries can be reviewed at all.
What You Get
- An assessment of the credential technology in use, and what it is actually worth.
- A reconciled access list, with every holder who should no longer have access named.
- Zones and time windows defined, so access is scoped rather than binary.
- Revocation inside the HR process, and contractor credentials that expire by themselves.
- A documented periodic review that satisfies an auditor and, more usefully, catches the accumulation nobody notices.
The question worth being able to answer is not whether you have badges. It is what happened to the badge of the person who left in March.