Cage or Rack-Level Restriction
Back to Data Center Management · Badge or Biometric Access · Access Logging · Visitor and Vendor Tracking · Service Offerings
This is in shared facilities, limiting access to your own footprint specifically. The reason it needs saying separately is that a colocation provider's security is genuinely good — and almost all of it protects the building, which you share with every other tenant, their staff, and their vendors.
1. Facility Access Is Not Equipment Access
The provider's perimeter, guards, mantraps and cameras keep out people who have no business in the building. They do not distinguish between you and the twelve other organisations who legitimately have business there, and whose contractors are in the hall today with a trolley.
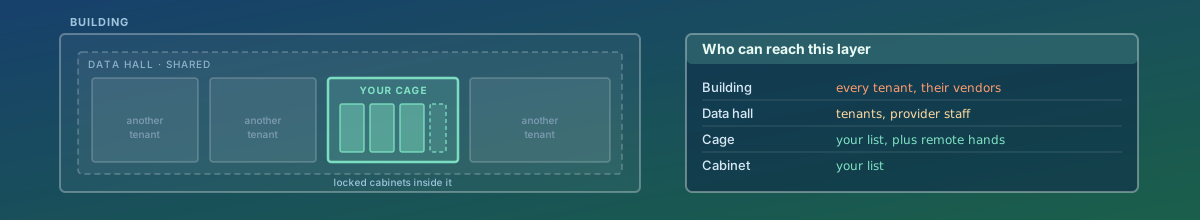
Access therefore has to be thought of in layers, as the illustration above sets out, with each layer answering who can reach this:
| Layer | Controlled by | Who is inside it |
|---|---|---|
| Building | The provider | Every tenant, their staff and their vendors |
| Data hall | The provider | Tenants with equipment in that hall, plus provider staff |
| Your cage or suite | You, ideally | Your access list, plus remote hands |
| The cabinet | You | Your access list |
The two bottom rows are the ones you own, and they are the ones most often left to the provider's list or to a key in a drawer.
2. A Cage Has to Be a Boundary, Not a Suggestion
- Mesh to the structural ceiling, not to the suspended one. A cage that stops at the tiles is a fence with a gap above it, and the gap is the easiest thing in the room to overlook because nobody looks up.
- Below the raised floor too. The void is continuous across the hall unless something stops it.
- Mesh fine enough that an arm does not reach equipment, and panels fixed so they cannot be unbolted from outside.
- Your own reader on the cage door, producing your own log. If entry to your space is recorded only by the provider, your audit trail is a support ticket away.
- A camera covering the cage door, either yours or with a contractual right to the footage within a stated time.
3. The Cabinet Lock Is Usually the Weak Link
Cabinets ship with locks, and that is roughly where the thinking stops. Two problems, both the shared-key problem from badge access wearing different clothes:
- Keyed alike. Cabinets from one manufacturer very often share a common key pattern, so the key from a cabinet in another hall opens yours. Where that is the case, the lock is a dust cover.
- No identity and no record. Even a unique key tells you nothing about who opened the door.
Electronic cabinet locks with per-person credentials and their own audit trail solve both, and are worth it for cabinets holding anything regulated. Where they are not justified, at minimum use unique keys, record who holds each, and treat the key register the way you treat the access list — including collecting them from leavers.
Side panels matter as well: adjacent cabinets with shared or removed side panels are one cabinet with two doors.
4. The Provider's Own Staff
This is not a suspicion, it is a design fact: remote hands exists so that somebody who does not work for you can physically touch your equipment at three in the morning. It is a genuinely useful service and it is also the broadest standing physical access anyone has to your estate.
- Know the policy. Who may enter your cage, under what authorisation, and whether a specific request is required each time.
- Require it to be logged and available to you, naming the individual.
- Scope it. Remote hands reseating a cable is different from remote hands opening a cabinet holding customer data. Where the distinction matters, the cabinet lock is what enforces it.
- Treat it as vendor access, with the obligations covered in visitor and vendor tracking.
5. Settle It in the Contract
Several of the controls above are not things you can install. They are things you must be entitled to, and the moment to establish that is before signing rather than during an incident.
- Access records for your space, including provider staff, available within a stated period.
- Who may authorise an addition to your access list — it should be a named role of yours, not a phone call from anyone claiming to be you.
- Notification when the provider's own access arrangements change.
- A right to audit, and sight of the facility's own attestation. A provider's SOC 2 report covers their controls, which become complementary user entity controls on your side — the things the report assumes you are doing, which is precisely this page.
- What happens at exit: how equipment leaves, and who confirms the cage is empty.
6. It Applies in Your Own Building Too
The same argument holds in a server room you own, with the tenants replaced by your own colleagues. Everyone with a reason to enter the room does not necessarily have a reason to open every cabinet — particularly where one holds systems in scope for an audit and the others do not. A locked cabinet inside a controlled room is the cheapest way to make that distinction real.
How We Approach It
- Establish who can reach each layer today, including the provider's staff and every tenant's vendors, and write it out as the table above.
- Inspect the physical boundary: above the ceiling, below the floor, the mesh, the panel fixings, the side panels.
- Check the cabinet locks, including whether they are keyed alike, and who holds keys.
- Put your own reader and record at the cage, so your audit trail does not depend on a third party.
- Scope and log remote hands, and decide which cabinets it may open.
- Close the contractual gaps, including the complementary user entity controls the provider's report assumes you operate.
What You Get
- A layer-by-layer statement of who can reach your equipment, which is usually more people than expected.
- A physical inspection of the cage boundary, including the two places nobody looks.
- A cabinet lock assessment, with the keyed-alike cabinets identified and a key register.
- Your own access record at the cage layer, independent of the provider's.
- The contractual terms you need, and a mapping of the provider's complementary user entity controls to what you actually do.
The question that makes this concrete: if someone opened one of your cabinets last night, would you find out, and would anybody be able to tell you who it was?